Splunk Security Content for Threat Detection & Response: August Recap
Security Splunk Threat Research TeamIn August, the Splunk Threat Research Team (STRT) had 2 releases of new security content via the Enterprise Security Content Update (ESCU) app (v6.4.0 and v6.5.0) With these releases, there are 2 new analytic stories, 40 new analytics, and 52 updated analytics, now available in Splunk Enterprise Security via the ESCU application update process.
Content highlights include:
- Linux Detection Coverage Expansion: Expanded Linux behavioral coverage targeting privilege escalation, persistence, execution, defense evasion, reverse shells, container abuse, and suspicious service activity. New analytics identify behaviors including bootloader and system file modification, shared-memory execution, UDEV and XDG persistence, privileged container execution, PostgreSQL and Redis abuse, Ghostscript exploitation, shell history access, and multiple potential privilege-escalation paths, giving defenders stronger visibility into suspicious activity that can blend with legitimate Linux administration.
- Windows Detection Coverage Expansion: Expanded Windows detection coverage with new analytics for network reconnaissance, suspicious PowerShell execution, and abnormal process behavior.
- RoguePlanet and ShieldBreak Coverage Update: Expanded the RoguePlanet analytic story with six new detections targeting Windows Defender race-condition exploitation and related ShieldBreak techniques.
- Malicious Python Package Installation: Introduced four detections covering abuse of the Python package installation lifecycle - identifying build-time network connections, executable .pth files, Python site hooks, and PYTHONPATH manipulation, helping defenders uncover supply-chain execution and persistence on workstations and build systems.
- Vidar Stealer Detection Coverage: New Vidar Stealer coverage that combines a detection for uncommon processes reading sensitive cloud profiles with browser credential and process analytics, helping defenders identify theft of credentials, cookies, and Azure CLI metadata before it enables account takeover or data exfiltration.
- Cross-Platform Detection Refinements: Updated 46 analytics across Windows, Linux, macOS, ESXi, and AWS Bedrock to improve detection fidelity and behavioral coverage. The refinements strengthen visibility into AI infrastructure abuse, credential access, browser data theft, process injection, persistence, privilege escalation, reconnaissance, security-tool tampering, and destructive activity, helping security teams investigate suspicious behavior across a broader range of endpoint, virtualization, and cloud telemetry.
Title
Related Articles
Filter
Category
Blog Limit
3
Category
security
Sort Category Shuffle Order
true
Related Articles
How to Marie Kondo Your Incident Response with Case Management & Foundational Security Procedures
Learn how successful security teams “Marie Kondo” their security operations, cleaning up their “visible mess” to identify the true source of “disorder” (the cyber attack itself).
Splunk SOAR Playbook of the Month: Threat Hunting with Playbooks
For this month’s edition of Playbook of the Month, we’ll look at how you can use Splunk SOAR’s Hunting playbook to perform threat hunting activities at machine speed.
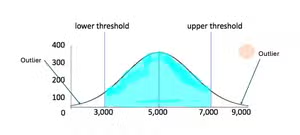
The Geometry of Fraud Detection
Splunker Nimish Doshi shares statistical ways to find outliers and visualizes what they would look like if using virtual area or virtual volume as geometric representations to find them.